
Cybersecurity
Fake Roblox executor steals data and lets attackers take control of infected devices
The campaign impersonates Xeno to infect devices with malware capable of stealing accounts, passwords and financial data, while also spying on victims.
- Fake Solana, Luno, and TradingView sites use In-browser JavaScript to deliver malware
- HalluSquatting: the new trick that uses AI assistants to install malware
- 1
Rheinmetall targets the frigate market, challenging Spain’s F-110 before production even begins
- 2
Chinese intelligence links Israel to Ceuta crisis as retaliation against Pedro Sánchez
- 3
A single comment can hijack your browser via AI
- 4
A new Sunni axis is reshaping the Muslim world’s security architecture
- 5
Ransom Cartel ransomware creator sentenced to 16 years in US prison
- Silvia Montes
- Security and Technology Editor
- Published on
10 August 2026 at 07:15
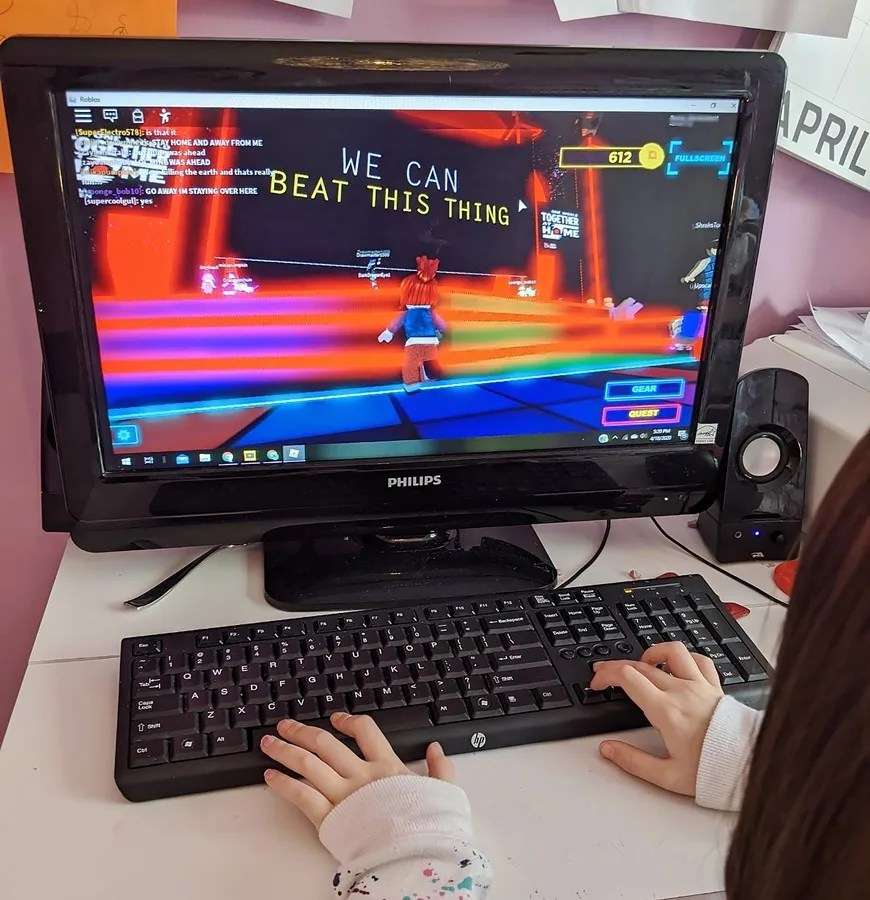
Bitdefender has warned of amalware campaign impersonating Xeno, a popular Roblox script executor that can be used to automate actions, run custom code and cheat. The threat is distributed through gaming forums and Discord communities, where it is presented as an “undetected” version capable of evading systems designed to block such tools.
Under this guise, it launches a multi-stage Java infection chaindesigned to make detection more difficult. Throughout the process, the malware attempts to maintain an appearance of legitimacy.
According to the cybersecurity company, its components imitate files from a Xeno installation, while later stages use Windows-like DLL names, trusted-looking directories and persistence mechanisms related to display settings.
After progressing through the various stages, the malware deploys a final payload that goes far beyond conventional credential theft, Bitdefender warns.
Data theft and remote control
According to the company, this payload combines the functions of an information stealer with those of a remote access trojan, or RAT, giving it surveillance capabilities and control over the infected device.
As aninformation stealer, it can steal browser cookies, Discord, Roblox and Minecraft accounts, cryptocurrency wallet data and payment-related tokens, potentially resulting in financial losses.
As aRAT, it can take screenshots, access the webcam, stream the victim’s desktop, and record keystrokes and mouse movements. It can also upload and download files, execute PowerShell commands and open an interactive console from which the attacker can enter commands directly and ultimately take control of the device.
“The malware can severely impact victims’ privacy because it gives attackers access to both stored personal information and real-time activity,” Bitdefender stresses.
Both the campaign and the malware continue to evolve
According to the cybersecurity company’s telemetry, the campaign has been affecting users since the beginning of 2026 and saw a sharp rise in activity during the second half of March. Infection levels have remained relatively stable since then, with the campaign not only remaining activebut continuing to evolve.
The malware used in this campaign had previously been documented under the name Powercat. However, Bitdefender researchers have identified new command-and-control infrastructure and additional capabilities, suggesting that the malware itself also remains under active development.
Risk to minors and users of shared computers
The campaign exploits the habit among many players of downloading mods, scripts and unofficial tools from Discord servers, forums and file-sharing platforms.
Bitdefender considers the threat particularly concerning because Roblox cheats can attract children and teenagers, potentially exposing accounts, private conversations, webcam images and financial information stored on shared family computers.
Avoiding unofficial tools: the first line of defense
To guard against this and similar campaigns, the company says the most effective protective measure is to avoid unofficial cheats and executors, particularly those distributed through untrusted websites, archive files, forums or unsolicited Discord messages.
Bitdefender also recommends combining up-to-date endpoint protection with reputation-based blocking, application-control policies, restrictions on software execution and multi-factor authentication. It further advises discussing common gaming-related scams with younger users, as recognizing these lures before executing the files can prevent account theft, financial losses and complete system compromise.
Become a premium member for free!
You may be interested in
- CybersecurityFake Solana, Luno, and TradingView sites use In-browser JavaScript to deliver malwareSergio Delgado Martorell
- CybersecurityHalluSquatting: the new trick that uses AI assistants to install malwareAlberto Payo
- CybersecurityChina launches investigation into US firm Palo Alto NetworksAlberto Payo
- CybersecurityAlleged security breach exposes over 5.2 million gym customer recordsAlberto Payo
“;
$(“#container-comentar-comentarios”).html(respuesta);
} else if (data == 2) { //TIEMPO
var respuesta =
“No ha pasado aún un minuto desde tu último comentario. Espera un poco y podrás comentar de nuevo una noticia.
“;
$(“#container-comentar-comentarios”).html(respuesta);
} else if (data == 3) { //PALABROTA
var respuesta = “Por favor, utiliza un lenguaje correcto para comentar las noticias.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
} else { //NO LOGUEADO
var respuesta =
“Lo sentimos, al parecer no tienes una sesión iniciada. Vuelve a Iniciar Sesión y podrás publicar este comentario.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
},
error: function(request, error) {
//console.log(error);
}
});
}
function sumarPositivo(id_comentario, id_usuario) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/sumar_reaccion_comentario.php?t=` +
generarCadenaAlfanumerica(),
data: {
tipo: ‘positivo’,
id_comentario: id_comentario,
id_usuario: id_usuario
},
success: function(data) {
//console.log(data);
if (data == 1) {
var likes = parseInt($(“#like_” + id_comentario + ” span”).text());
$(“#like_” + id_comentario + ” span”).text(parseInt(likes + 1));
}
},
error: function(request, error) {
//console.log(error);
}
});
}
function sumarNegativo(id_comentario, id_usuario) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/sumar_reaccion_comentario.php?t=` +
generarCadenaAlfanumerica(),
data: {
tipo: ‘negativo’,
id_comentario: id_comentario,
id_usuario: id_usuario
},
success: function(data) {
//console.log(data);
if (data == 1) {
var dislikes = parseInt($(“#dislike_” + id_comentario + ” span”).text());
$(“#dislike_” + id_comentario + ” span”).text(parseInt(dislikes + 1));
}
},
error: function(request, error) {
//console.log(error);
}
});
}
function recargar_widgets_sesion() {
recargar_cabecero_sesion();
recargar_menu_sesion();
recargar_comentar_sesion();
recargar_comentar_comentar();
comprobar_user_sesion_215_articulo(0);
}
function iniciarSesion() {
var continuar = true;
var msg = “”;
var usuario_log = $(“#usuario_log”).val();
var password_log = $(“#password_log”).val();
var valor_periodico = $(‘#valor_periodico’).val();
// console.log(valor_periodico);
if (usuario_log.length == 0) {
continuar = false;
msg += “Es necesario rellenar el correo electrónico n”;
}
if (password_log.length == 0) {
continuar = false;
msg += “Es necesario rellenar la contraseña.n”;
}
if (continuar) {
$.ajax({
type: “POST”,
data: $(“#formulario_login”).serialize(),
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/login-user.php?t=` +
generarCadenaAlfanumerica(),
success: function(data) {
// console.log(data);
if (data == 1) {
recargar_widgets_sesion();
$(“#modal-login .modal-action.modal-close.close-btn”).trigger(“click”);
$(“#usuario_log”).val(“”);
$(“#password_log”).val(“”);
if (window.location.href.includes(“area-usuario”)) {
// window.location.reload();
}
} else {
var respuesta =
“No hemos encontrado ningún usuario con el correo electrónico y la contraseña introducidos. Por favor, vuelve a intentarlo o recupera la contraseña pulsando el botón inferior.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
}
});
} else {
Swal.fire({
text: msg,
icon: “warning”
});
}
}
function comprobar_user_sesion_215_articulo(es_premium) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/comprobar_sesion_user.php?t=` +
generarCadenaAlfanumerica(),
success: function(data) {
console.log(“COMPROBADO SESION USUARIO ” + data);
if (data == 1) {
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).removeClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).addClass(“d-none”);
$(“#banner-premium”).addClass(“d-none”);
} else {
// $(“#art-cuerpo-visible”).removeClass(“art-cuerpo-visible”);
// $(“#art-cuerpo-visible”).addClass(“art-cuerpo-no-visible”);
if (es_premium) {
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“d-none”);
$(“#art-cuerpo-visible-premium”).addClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).removeClass(“d-none”);
$(“#banner-premium”).removeClass(“d-none”);
} else {
$(“#art-cuerpo-visible-premium”).removeClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).addClass(“d-none”);
$(“#banner-premium”).addClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“art-cuerpo-visible”);
}
}
}
});
}
function comprobar_user_sesion_215() {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/comprobar_sesion_user.php?t=` +
generarCadenaAlfanumerica(),
success: function(data) {
console.log(“COMPROBADO SESION USUARIO ” + data);
if (data == 1) {
$(‘.col-comparador-registro-login’).addClass(‘w-auto’)
} else {
$(‘.col-comparador-registro-login’).removeClass(‘w-auto’)
}
}
});
}
function cerrarSesion() {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/delete-session-user.php?t=` +
generarCadenaAlfanumerica(),
success: function(data) {
//console.log(data);
recargar_widgets_sesion();
$(“#offCanvasClose”).trigger(“click”);
if (window.location.href.includes(“area-usuario”)) {
window.location.href = ‘/’;
}
}
});
}
function registrarCuenta() {
var continuar = true;
var msg = “”;
var email_registro = $(“#email_reg”).val();
var pass_registro = $(“#password_reg”).val();
var pass_registro2 = $(“#password_reg_2”).val();
var nombre_registro = $(“#nombre_reg”).val();
var apellidos_registro = $(“#apellidos_reg”).val();
var ref_id_periodico = $(“#ref_id_periodico”).val();
if (pass_registro2 != pass_registro) {
continuar = false;
msg += “Deben coincidir ambas contraseñas. n”;
}
if (email_registro.length == 0) {
continuar = false;
msg += “Es necesario rellenar el correo electrónico. n”;
}
// if (pass_registro.length = 8) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
data: $(‘#resetear-clave’).serialize(),
url: `https://api.v.1.2.3.escudodigital.newscript.es/api/resetear-pass.php?t=` +
generarCadenaAlfanumerica(),
success: function(data) {
//console.log(data);
$(“#email_recuperar”).val(“”);
var respuesta = “La contraseña se ha actualizado. Ya puedes volver a Iniciar Sesión.”;
Swal.fire({
text: respuesta,
icon: “success”
}).then((result) => {
window.location.href = ‘http://www.escudodigital.com/’;
});
}
});
} else {
var respuesta = “La contraseña debe tener un mínimo de 8 caracteres.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
} else {
var respuesta = “Ambas contraseñas deben coincidir.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
}
$(document).ready(function() {
recargar_widgets_sesion(); //DESCOMENTAR ESTO
});
‘)
.text(msg)
.insertAfter($el);
}
function esEmailValido(email) {
return /^[^s@]+@[^s@]+.[^s@]{2,}$/.test(String(email).trim());
}
function validar() {
limpiarErrores();
let ok = true;
const $nombre = $(“#nombre”);
const $email = $(“#email”);
const $motivo = $(“#motivo”);
const $check = $(“#checkbox”);
const nombre = $nombre.val().trim();
const email = $email.val().trim();
const motivo = $motivo.val().trim();
if (nombre.length Message sent successfully.
‘);
$form[0].reset();
} else {
$(“#msgFormContacto”).html(‘Message not sent. Try again.
‘);
}
})
.fail(function(xhr) {
$(“#msgFormContacto”).html(‘Connection error. Try again.
‘);
})
.always(function() {
setLoading(false);
});
}
$btn.on(“click”, function(e) {
e.preventDefault();
e.stopPropagation(); // Stop default button behavior if any
if (!validar()) return;
// Execute reCAPTCHA
if (window.grecaptcha) {
grecaptcha.ready(function() {
grecaptcha.execute(RECAPTCHA_SITE_KEY, {
action: ‘submit’
}).then(function(token) {
submitFormWithToken(token);
});
});
} else {
// Fallback or error if grecaptcha not loaded
alert(“reCAPTCHA not loaded. Please refresh.”);
}
});
$(“#nombre,#email,#motivo,#checkbox”).on(“input change”, function() {
$(this).removeClass(“is-invalid”);
$(this).next(“.error-text”).remove();
});
});
